01
Security Tools / Data Sources
Monitor, prioritize, and respond with AI-assisted triage
A security operations dashboard that normalizes events, scores risk, prioritizes alerts, and routes human-approved response workflows.
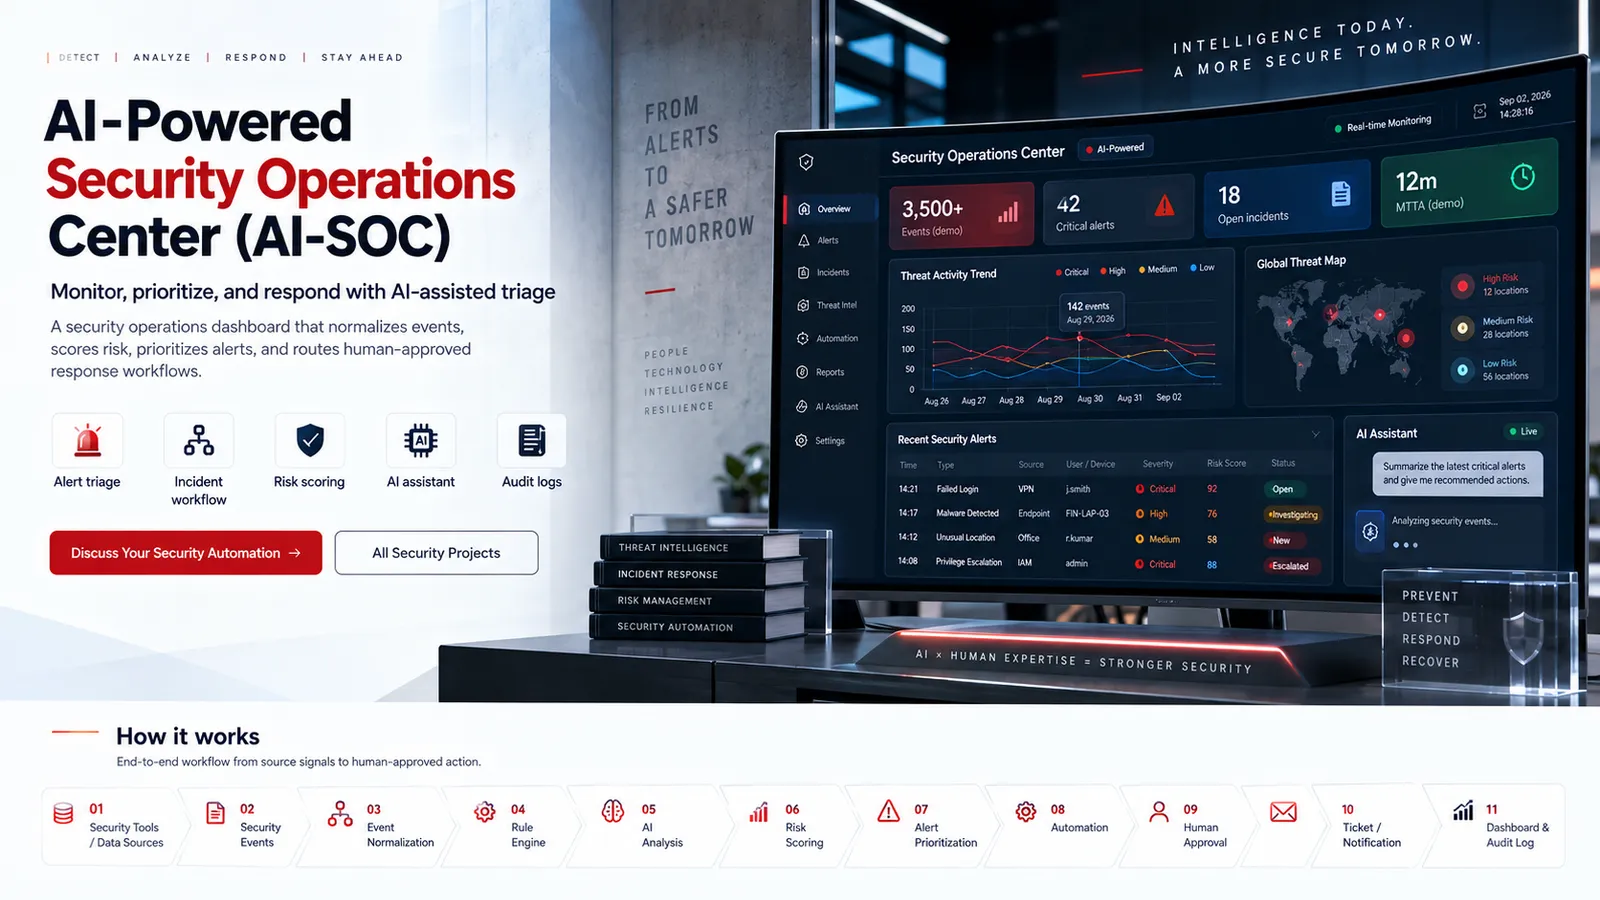
3,500+
Events (demo)
42
Critical alerts
18
Open incidents
12m
MTTA (demo)
Security teams drown in noisy alerts across tools. Analysts spend hours triaging low-value events while critical incidents wait — without a unified view, correlation, or consistent response process.
A reference AI-SOC workspace that ingests security events, applies rules and AI analysis, scores risk, prioritizes work, opens tickets/notifications, and keeps an audit trail — with humans approving high-risk actions.
End-to-end workflow from source signals to human-approved action and audit logging.
01
Security Tools / Data Sources
02
Security Events
03
Event Normalization
04
Rule Engine
05
AI Analysis
06
Risk Scoring
07
Alert Prioritization
08
Automation
09
Human Approval
10
Ticket / Notification
11
Dashboard & Audit Log
Demo KPIs for total events, critical/high/medium alerts, open vs resolved incidents, MTTA/MTTR, and risk/incident trends.
Filterable alert table with ID, timestamp, type, source, user/device, IP, severity, risk score, status, and assignee.
Simulated AI explains what happened, why it was detected, affected assets, related events, investigation steps, recommended response, and confidence.
Statuses from New → Investigating → Escalated → Contained → Resolved → Closed with notes, assignment, and escalation.
Example correlations such as failed login + new device + unusual location + multiple attempts → potential account compromise.
Suspicious login → detect → score → alert → notify → ticket, with audit logs and executive security summaries.
Metrics and screens below are simulated for demonstration. Not live customer telemetry.
Integration capabilities with common security and IT systems — not claimed vendor partnerships.
Other portfolio demonstrations of customized security automation.
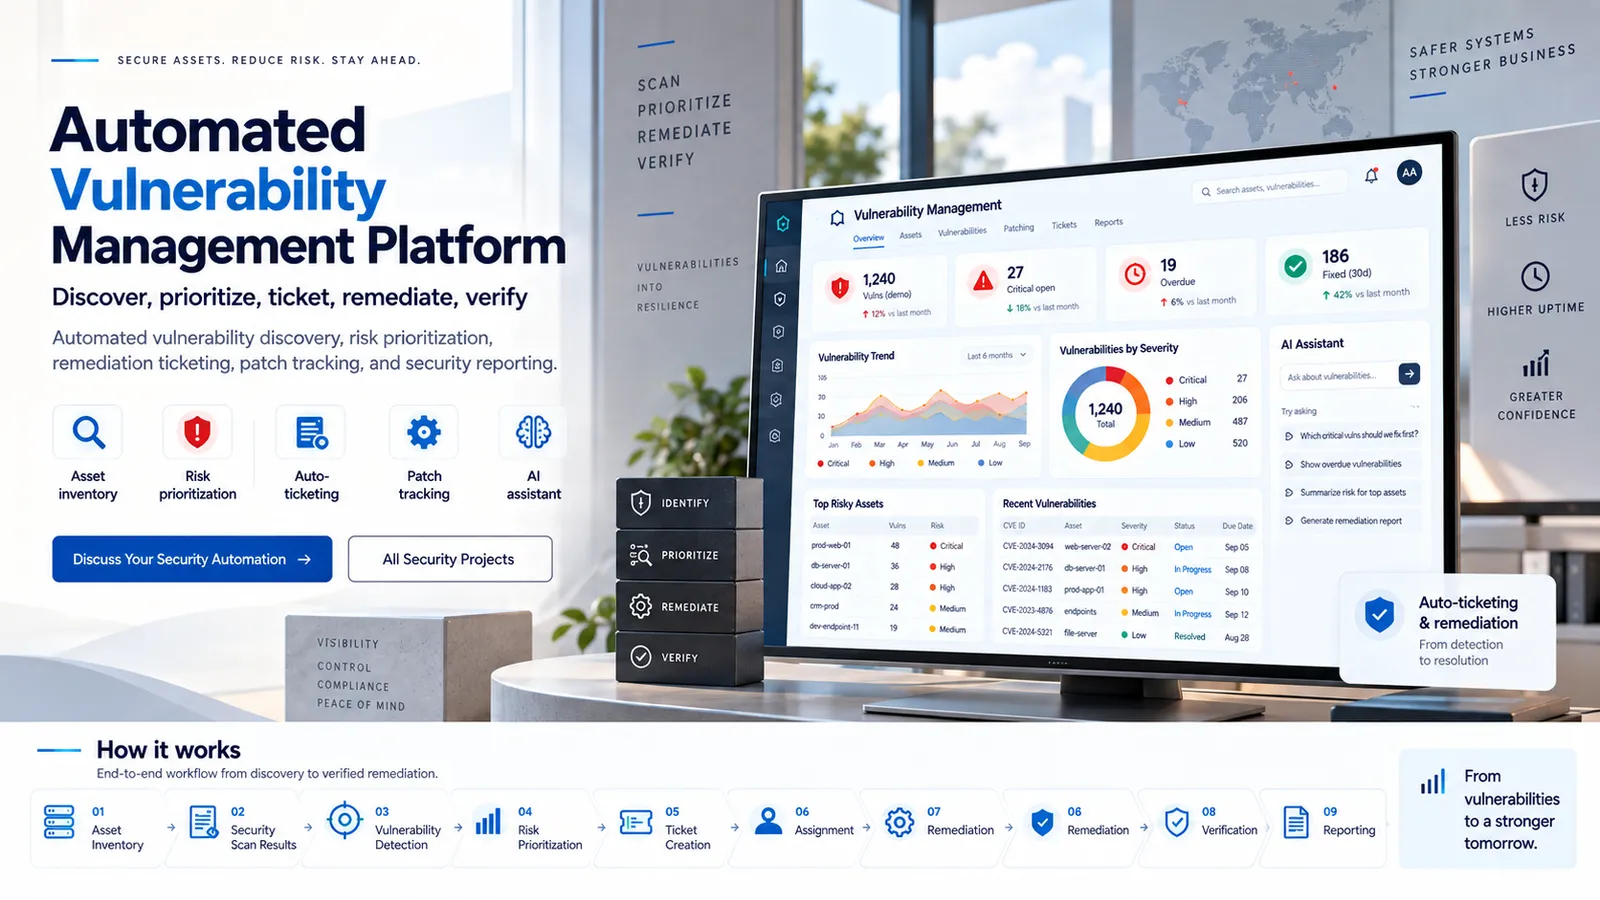 Vulnerability Management
Automated vulnerability discovery, risk prioritization, remediation ticketing, patch tracking, and security reporting.
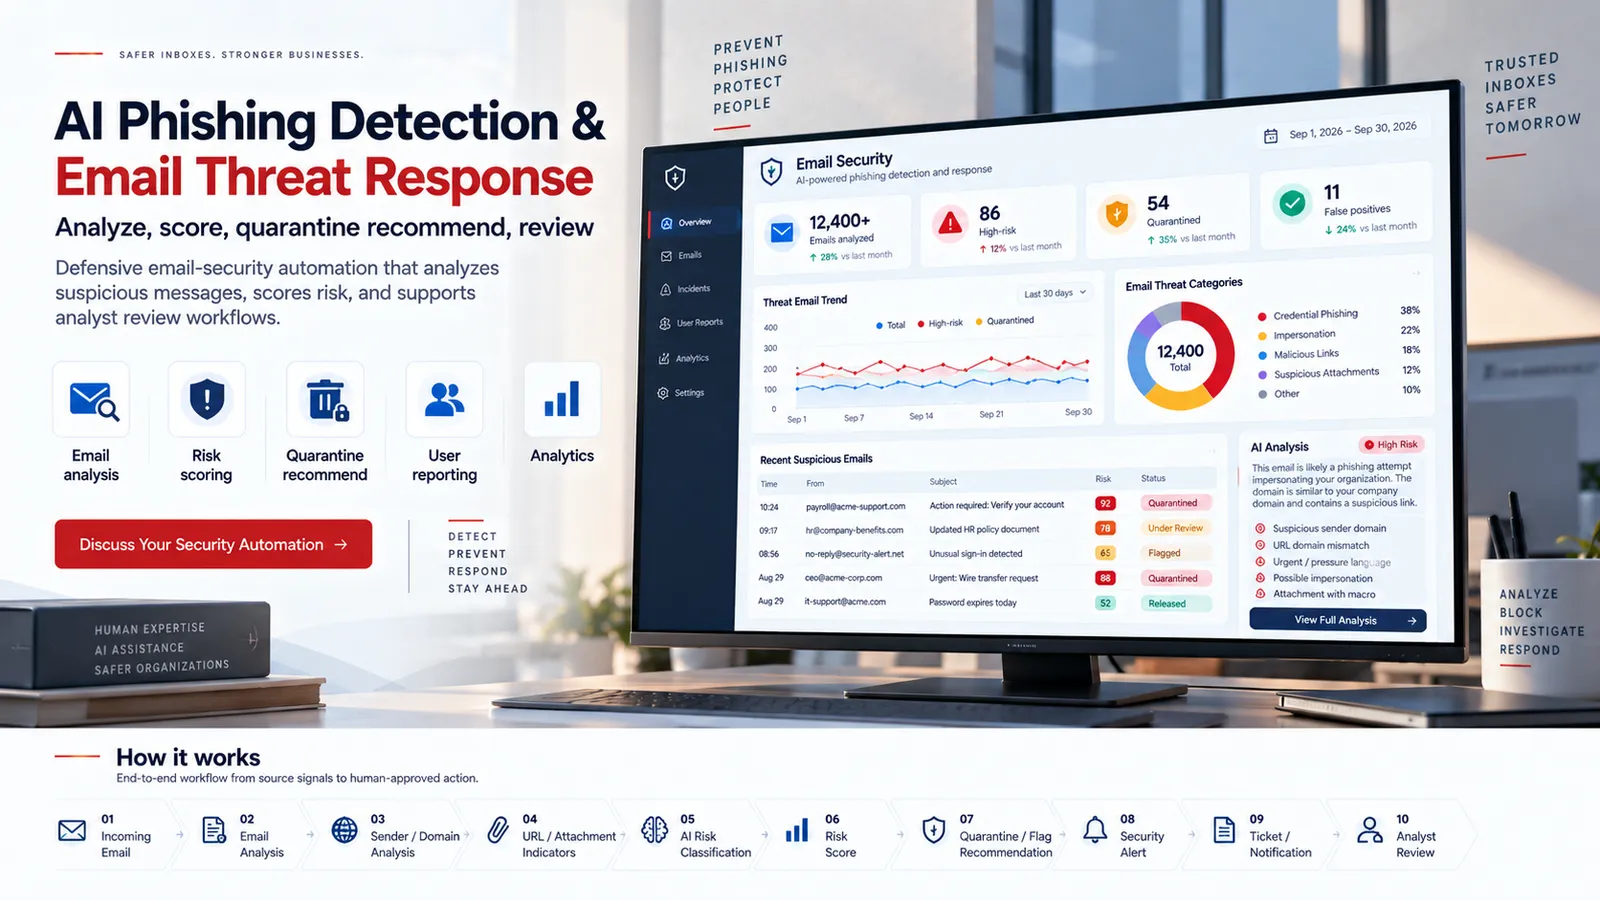 Email Security
Defensive email-security automation that analyzes suspicious messages, scores risk, and supports analyst review workflows.
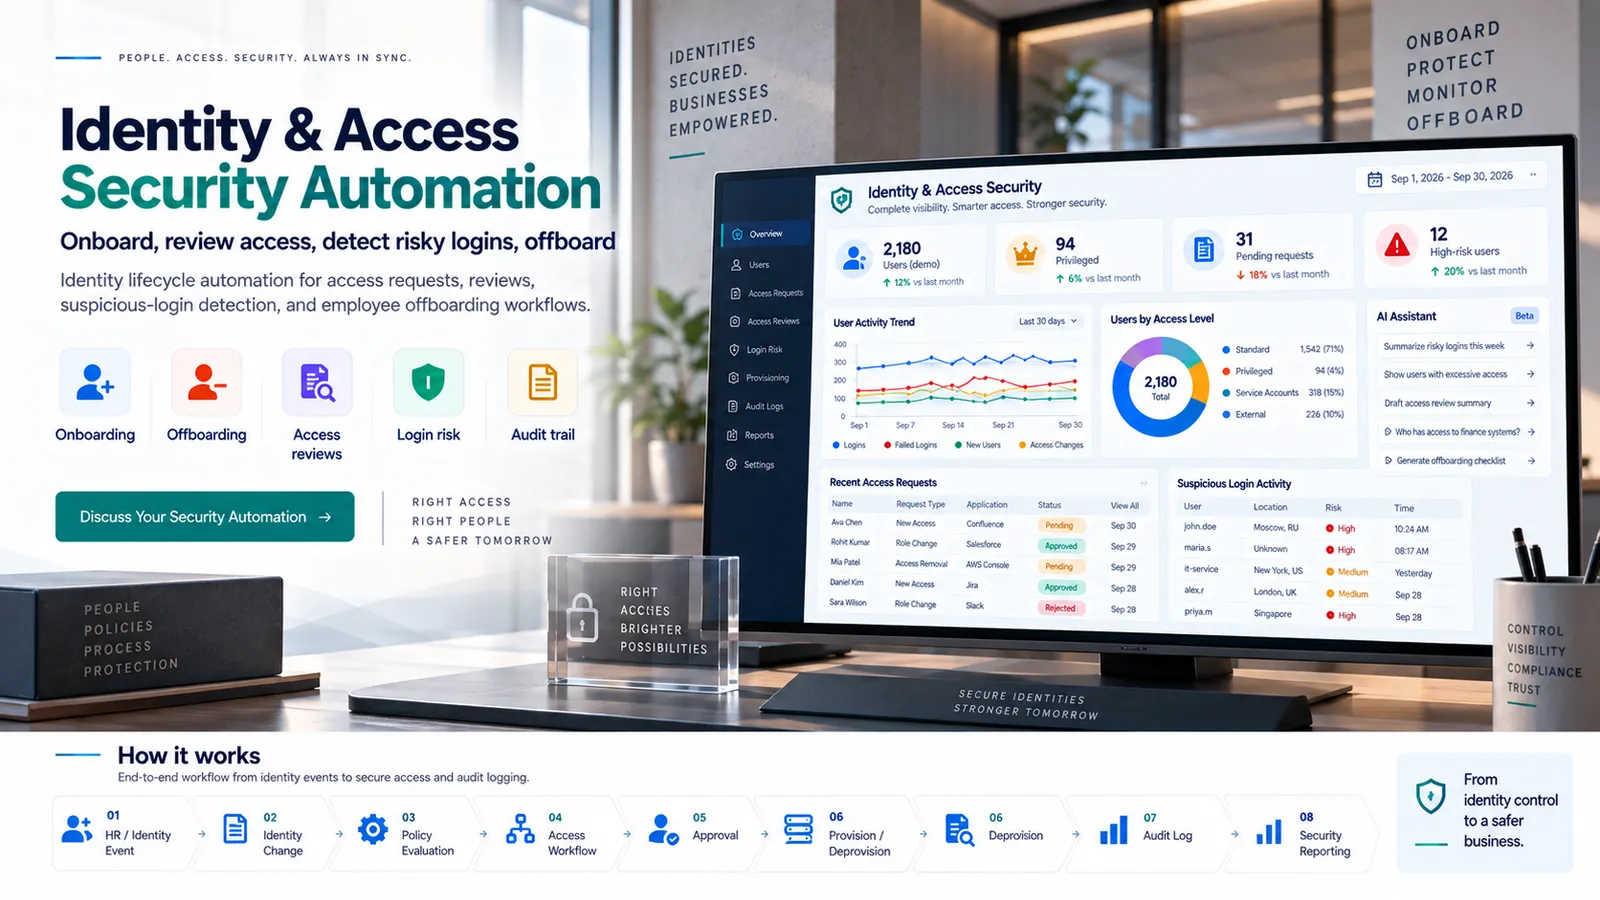 Identity Security
Identity lifecycle automation for access requests, reviews, suspicious-login detection, and employee offboarding workflows.
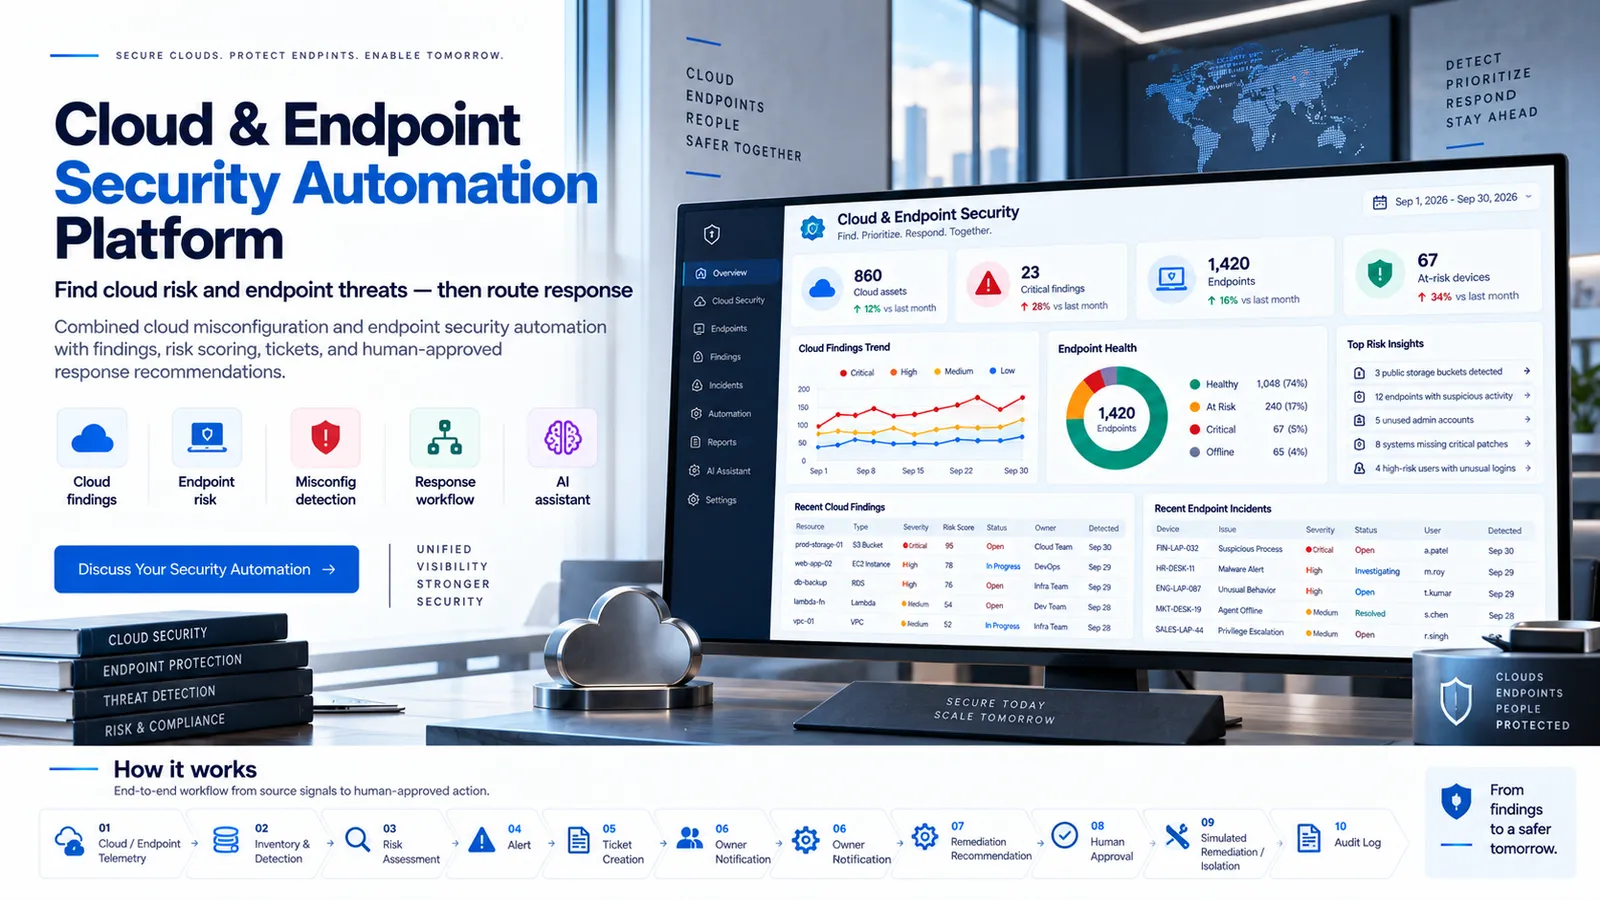 Cloud & Endpoint
Combined cloud misconfiguration and endpoint security automation with findings, risk scoring, tickets, and human-approved response recommendations.
Explore a custom security automation solution tailored to your tools and approval model.